GUTSCHEIN
Bitte haben Sie einen Moment Geduld, wir legen Ihr Produkt in den Warenkorb.
Diese Produkte könnten Sie auch interessieren:
Bitte haben Sie einen Moment Geduld, wir legen Ihr Produkt in den Warenkorb.
| ISBN | 9798193513223 |
|---|---|
| Sprache | Englisch |
| Erscheinungsdatum | 18.08.2026 |
| Größe | 229 x 152 mm |
| Verlag | Amazon Digital Services LLC - Kdp |
| Lieferzeit | Lieferung innerhalb von 28 Werktagen |
| Herstellerangaben | Anzeigen Libri GmbH Europaallee 1 | D-36244 Bad Hersfeld gpsr@libri.de |
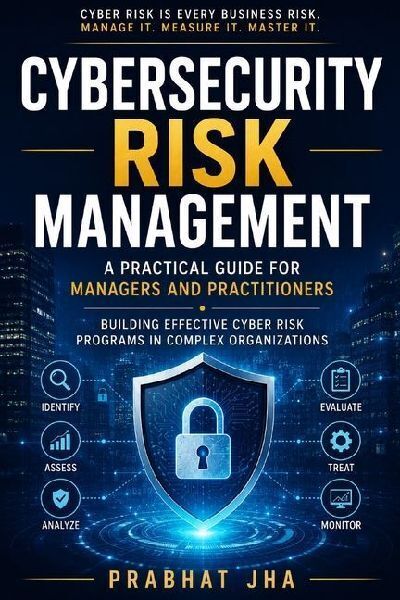
Cyber risk is no longer just an IT problem. It is a business risk that can disrupt operations, damage customer trust, create regulatory exposure, and threaten organizational resilience.Cybersecurity Risk Management: A Practical Guide for Managers and Practitioners provides a practical, decision-focused approach to understanding, assessing, treating, monitoring, and governing cyber risk in complex organizations.Rather than treating cybersecurity as a collection of technical controls, this book explains how to connect cyber risk with business objectives, risk appetite, governance, enterprise risk management, and executive decision-making.Inside, readers will learn how to: - Understand the nature and business impact of modern cyber risk- Apply core risk-management principles to cybersecurity- Use NIST CSF 2.0, ISO/IEC 27001 and 27005, FAIR, CIS Controls, and complementary frameworks- Establish context, scope, risk appetite, and risk criteria- Identify and value critical assets and understand threat and vulnerability exposure- Conduct qualitative and quantitative cyber risk analysis- Evaluate, prioritize, and treat cyber risks- Understand residual risk and make informed risk-acceptance decisions- Build effective cyber risk governance and accountability- Develop a risk-aware organizational culture- Integrate cybersecurity risk with enterprise risk management- Design meaningful metrics, reporting, and board-level communication- Manage third-party, supply-chain, cloud, hybrid, insider, and emerging-technology risks- Address ransomware, business continuity, disaster recovery, and cyber resilience- Navigate regulatory, legal, and compliance considerations- Design and implement a practical cyber risk management programThe book also includes industry case studies, discussion questions, practical templates, risk registers, qualitative assessment worksheets, FAIR analysis guidance, control-mapping references, a glossary, recommended resources, and a sample board reporting template.Written for managers, risk owners, cybersecurity and risk practitioners, governance professionals, internal auditors, technology leaders, and other professionals who need to translate technical cyber issues into meaningful business decisions, this book emphasizes a central principle: Cyber risk cannot be eliminated. It must be understood, prioritized, treated, accepted consciously, monitored, and governed.
| ISBN | 9798193513223 |
|---|---|
| Sprache | Englisch |
| Erscheinungsdatum | 18.08.2026 |
| Größe | 229 x 152 mm |
| Verlag | Amazon Digital Services LLC - Kdp |
| Lieferzeit | Lieferung innerhalb von 28 Werktagen |
| Herstellerangaben | Anzeigen Libri GmbH Europaallee 1 | D-36244 Bad Hersfeld gpsr@libri.de |
Wie gefällt Ihnen unser Shop?
